32kActiveWindows · Mac · LinuxMITReplaces partlyFor developers
Nuclei is a free command-line tool that checks websites, servers and networks for known security weaknesses. It is aimed at security professionals and IT teams, who write or reuse simple text-based templates to define each check.
6.8kActiveLinuxGPL-3.0Replaces partlyRuns on your own server
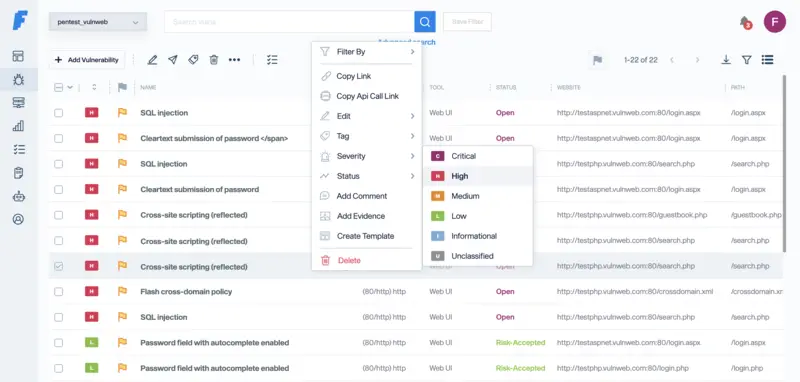
Faraday is a self-hosted platform that gathers security scan results from many tools into one place so teams can track and fix vulnerabilities. It is for security professionals and the managers and analysts who work with their findings.
5.3kActiveApache-2.0Replaces partlyRuns on your own server
ThreatMapper is a security tool that scans running cloud, container and server systems for software vulnerabilities, exposed secrets and risky configurations. It is aimed at security and operations teams who watch production infrastructure.
Runs on your own server · GitHub
None of these match. Try another device.
Before you build
Planning something for an alternative to Plextrac? See what exists first, so you can reuse parts or explain what's different. Paste this into any AI assistant:
Read the list of open-source alternatives at https://opensourceeverything.org/data/groups/security-scanning.json. Compare it with my project or idea below. Tell me which projects overlap, what I could reuse instead of rewriting, and what mine does that none of them do.
My project or idea:
Here is a list of open-source alternatives to Plextrac, from Open Source Everything (CC BY-SA 4.0):
- Nuclei (MIT, https://github.com/projectdiscovery/nuclei; replaces partly): Nuclei is a free command-line tool that checks websites, servers and networks for known security weaknesses. It is aimed at security professionals and IT teams, who write or reuse simple text-based templates to define each check.
- Faraday (GPL-3.0, https://github.com/infobyte/faraday; replaces partly): Faraday is a self-hosted platform that gathers security scan results from many tools into one place so teams can track and fix vulnerabilities. It is for security professionals and the managers and analysts who work with their findings.
- Deepfence ThreatMapper (Apache-2.0, https://github.com/deepfence/ThreatMapper; replaces partly): ThreatMapper is a security tool that scans running cloud, container and server systems for software vulnerabilities, exposed secrets and risky configurations. It is aimed at security and operations teams who watch production infrastructure.
Compare it with my project or idea below. Tell me which projects overlap, what I could reuse instead of rewriting, and what mine does that none of them do.
My project or idea: